> For the complete documentation index, see [llms.txt](https://angellm.gitbook.io/hacknotes/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://angellm.gitbook.io/hacknotes/htb/2023/analytics.md).

# Analytics

\#docker, #linux, #overlayfs

[**Analytics**](https://app.hackthebox.com/machines/Analytics) is an **EASY** machine from the Hack The Box platform. In it we will exploit an **RCE** thanks to an outdated version of a web tool. We will also perform a **Docker breakout**, to finally obtain root permissions thanks to the exploitation of a vulnerability in the **kernel version**.

***

### Enumeration <a href="#user-content-enumeration" id="user-content-enumeration"></a>

Let’s start by scanning the open TCP ports of the target machine:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FKsbVyzrV7x6O3LDdQ73W%2Fimage.png?alt=media&amp;token=dbf0c58a-0eda-40bd-aaf1-a08909df4536" alt=""><figcaption></figcaption></figure>

**nmap** reported tcp ports 22(ssh) and 80(http) to be open. Let’s scan them further:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FVqVpKu8F3qC6htHurwtg%2Fimage.png?alt=media&amp;token=22ef1272-90e2-4f89-ba3f-e1ba00ec0150" alt=""><figcaption></figcaption></figure>

**nmap** exhaustive scan reported that the service running on port 22 is OpenSSH 8.9p1. According to lauchpad, the target machine OS may be Ubuntu Jammy:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2F3dIhzk5YJclC8NR53MAq%2Fimage.png?alt=media&amp;token=2e2dfd27-9299-4de6-ace4-e982c0b0851e" alt=""><figcaption></figcaption></figure>

Regarding the http service on port 80, the service running is **nginx 1.18.0**. The scan also reported that a redirection may be being applied to <http://analytical.htb>, so the server may be applying virtual hosting. Before adding this domain to the **/etc/hosts** file, let’s check quickly the petition to the website using Burpsuite:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FwWzE41fA9BL1WKdu2b0D%2Fimage.png?alt=media&amp;token=a87d454a-3939-4d38-836d-9907d941beba" alt=""><figcaption></figcaption></figure>

As we can expect, the website is applying the redirection, and there is no information here we can use. So, let’s add the domain to **/etc/hosts** file:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FNrrjAiJXxz31SH1Rcbe0%2Fimage.png?alt=media&amp;token=2a084733-dfac-4db7-9a84-f5057a6cede8" alt=""><figcaption></figcaption></figure>

The **nmap** script **http-enum** didn’t find any common file in the server.

Let’s see what technologies are being used in the website apart from nginx:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FGuFG14IYS0pzkSvyDtIa%2Fimage.png?alt=media&amp;token=383669f3-a7cf-484d-bd79-61a63bc087cd" alt=""><figcaption></figcaption></figure>

The **whatweb** tool reports 2 email addresses (<demo@analytical.com> and <due@analytical.com>). It also reports that the website is using JQuery v3.0.0. This version of JQuery is outdated and is vulnerable to XSS.

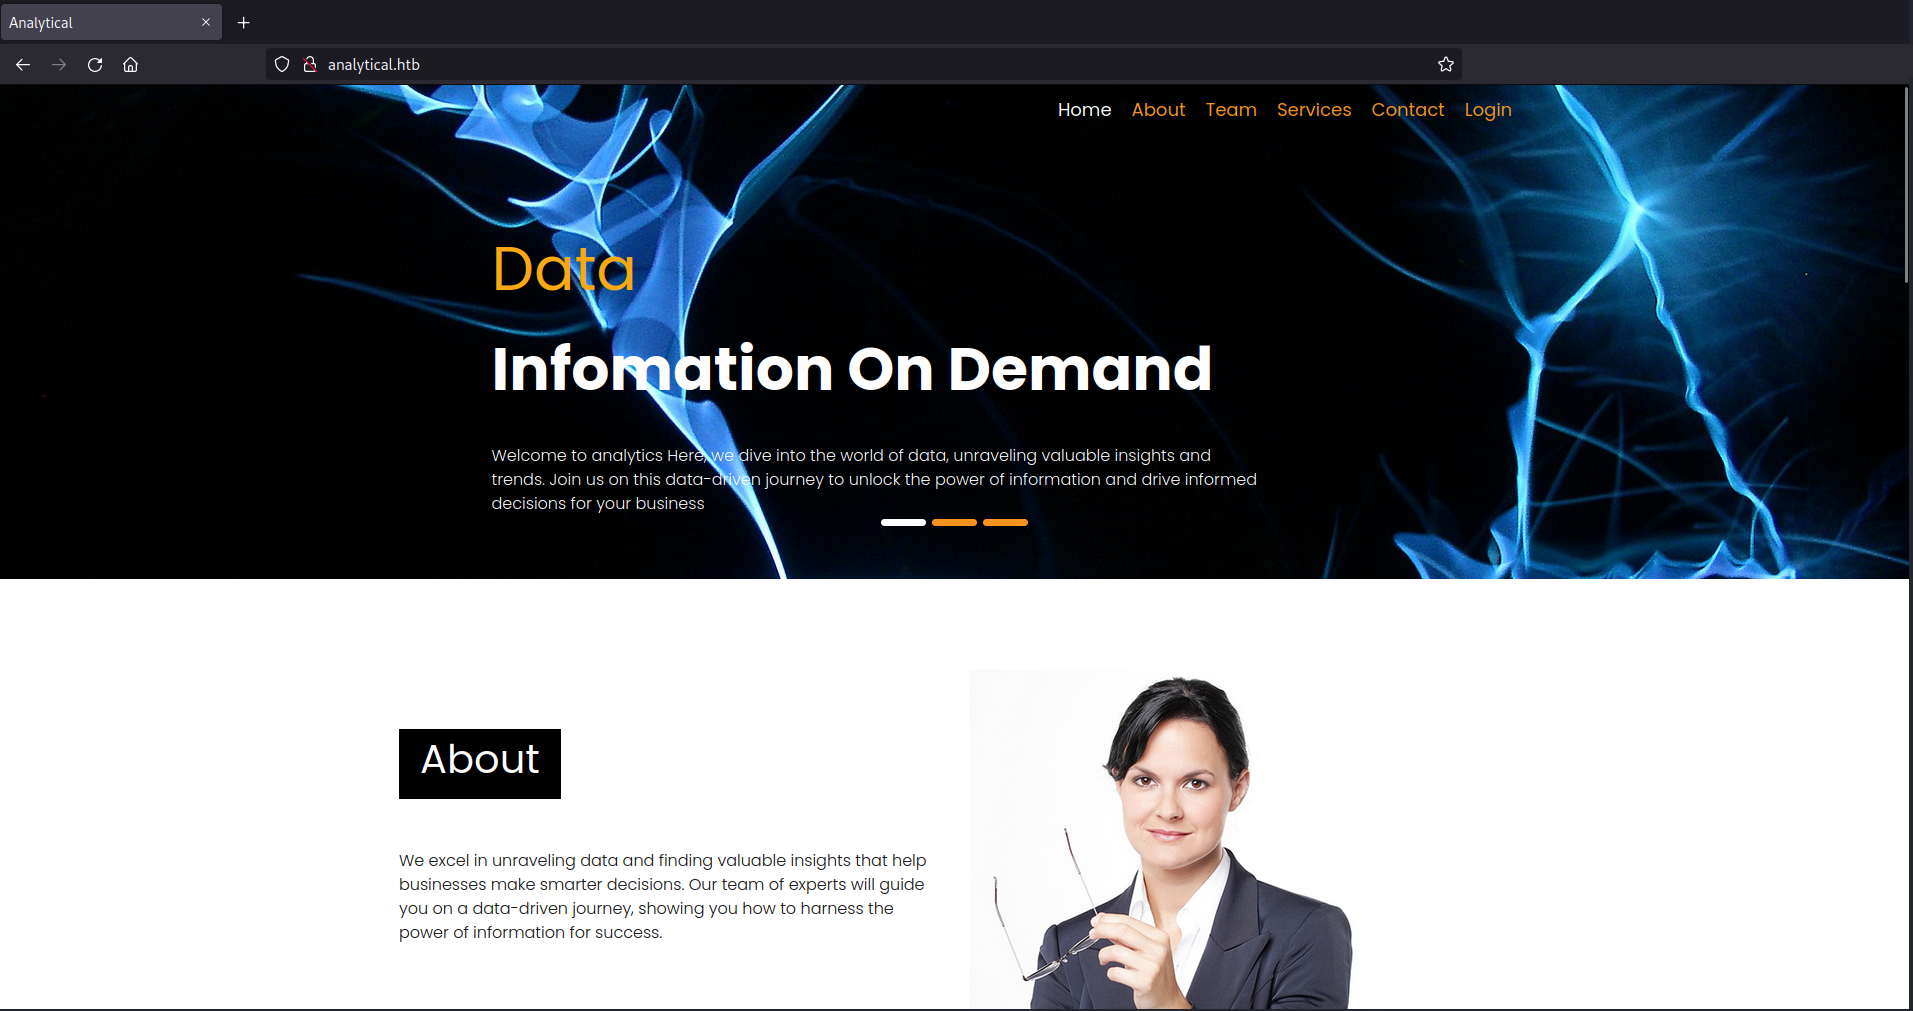
Let’s see how this page looks using the browser:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2Fgit-blob-9d64df4e59f89eaec28256ed677dcfa165bf6bf6%2Fanalytics6.png?alt=media" alt=""><figcaption></figcaption></figure>

There is a section called “Our Team” that shows photos, names and positions of workers. Let’s write down this data that may be useful to check usernames.

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FXjFXeUJmh3sV64mG2pfL%2Fimage.png?alt=media&amp;token=f56f5dbd-c203-4f94-b2d4-9f4a0116be88" alt=""><figcaption></figcaption></figure>

```
Jonny Smith - Chief Data Officer
Alex Kirigo - Data Engineer
Daniel Walker - Data Analyst
```

There is a contact form at the bottom on the page that doesn’t seem to work.

By hovering the top menu “Login” link we can see that it will redirect us to <http://data.analytical.htb>

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FiAoU9OT73mgZZk6BrACD%2Fimage.png?alt=media&amp;token=2e64950a-cd2b-405b-a60e-ef71c375606d" alt=""><figcaption></figcaption></figure>

Let’s add this subdomain in the **/etc/hosts** file.

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FAhJ2YdBJK3NItnOUy8gd%2Fimage.png?alt=media&amp;token=47ec580f-fee0-4368-aedd-4cac0a3d24b7" alt=""><figcaption></figcaption></figure>

Now, let’s click on the link:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FkBt9OhGxFqaolYrYK6vg%2Fimage.png?alt=media&amp;token=6a4af1e8-3f31-413c-96dc-785ed4c5b037" alt=""><figcaption></figcaption></figure>

It redirects us to a website where there is a service called Metabase. Let’s search what is this:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FUgnMWdUQLXIyVOXy0L6J%2Fimage.png?alt=media&amp;token=9ae3ba15-b797-42d8-9586-57947b5d179a" alt=""><figcaption></figcaption></figure>

## Exploitation <a href="#user-content-exploitation" id="user-content-exploitation"></a>

After some research, I found this interesting blog entry at MetaBase’s official webpage:

<https://www.metabase.com/blog/security-incident-summary\\\\>

In this blog is explained that there were some programming errors that made the application vulnerable in older versions of it.

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FENYOhZ4nnQ1e80EWJdXz%2Fimage.png?alt=media&amp;token=f5e80558-38c0-4363-aa96-f32172eff79c" alt=""><figcaption></figcaption></figure>

Checking for the setup token in the website of the target machine I found it:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FLv01OpxeSUsxTSKcgV2h%2Fimage.png?alt=media&amp;token=30198c61-7e00-4f9e-97c2-223c7243b3eb" alt=""><figcaption></figcaption></figure>

So, maybe the version of MetaBase is outdated and it is vulnerable.

I found this script written in Python that automates the exploitation process: <https://github.com/robotmikhro/CVE-2023-38646>

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FTra680NvcVIL65kpvq05%2Fimage.png?alt=media&amp;token=ec4065fb-ff44-4408-a026-f0e426506833" alt=""><figcaption></figcaption></figure>

After exploiting it, we gained a reverse shell!

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FMc0vxB8SOpc2dhsZ9iqt%2Fimage.png?alt=media&amp;token=ea20429b-8e98-47d8-8618-812a4e568451" alt=""><figcaption></figcaption></figure>

But it seems that we are inside a docker container. Let’s see how can we escape from it.

## Docker breakout <a href="#user-content-docker-breakout" id="user-content-docker-breakout"></a>

If we check the environmental variables with <kbd>env</kbd>:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FkD0dhpZ8mSqshRhYyoba%2Fimage.png?alt=media&amp;token=1bfe180f-a252-4485-ae74-9b5f251c60d6" alt=""><figcaption></figcaption></figure>

We can find the credentials `metalytics:AnXXXXXXXXXX223#`.

Let’s try to check if they are valid to connect to the target machine via ssh:

Yes, the credentials are valid.

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2F2yx4AJi36zctetgO9HoN%2Fimage.png?alt=media&amp;token=36415676-4465-4885-95fb-c34b62dfe653" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FWfMeY2kADx0lOuqGMHOE%2Fimage.png?alt=media&amp;token=fafd0b9c-a69b-42f2-aace-821af0ebe04c" alt=""><figcaption></figcaption></figure>

And that’s how we got the user flag

## Privilege Escalation <a href="#user-content-privilege-escalation" id="user-content-privilege-escalation"></a>

Let’s see the version of the Ubuntu and the kernel:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FZuDZ38AeIhU5gs11tRJz%2Fimage.png?alt=media&amp;token=f4ba135d-c670-4aad-b15f-1e2256def92f" alt=""><figcaption></figcaption></figure>

It’s an Ubuntu jammy, as we guessed in the enumeration phase. The Linux kernel is 6.2.0.

If we search for vulnerabilities of this kernel, we find this page: <https://www.wiz.io/blog/ubuntu-overlayfs-vulnerability>

In that article is explained that multiple versions of the linux kernel have a vulnerability related to the OverlayFS module that can be used to perform a Privilege Escalation. Apparently a similar vulnerability was detected and fixed back in 2021, but it happened again.

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FdhS7JmEyitfSQ0iUSEyW%2Fimage.png?alt=media&amp;token=2f6d6990-3f6a-4b4e-9c9c-1b03ac572a4a" alt=""><figcaption></figcaption></figure>

According to the article, the version of the kernel that the target Ubuntu is using is vulnerable.

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FziL9QoSpLYpBrLt6q4RX%2Fimage.png?alt=media&amp;token=25972de0-f5c2-4386-b156-b6820da2aae7" alt=""><figcaption></figcaption></figure>

The article also says that the old exploits still work for this vulnerability, so I’m going to use this one I found:

<https://github.com/briskets/CVE-2021-3493>

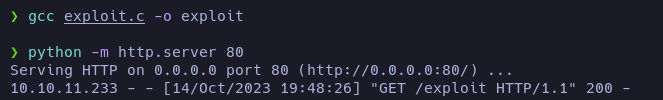
So, I downloaded the .c file and compiled it in my machine. Then I shared it with the target machine using an http server:

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2FGmNescwfATzWGc3AHSyH%2Fimage.png?alt=media&amp;token=c6ea5e7d-dd7e-4434-9662-7b765a2339a4" alt=""><figcaption></figcaption></figure>

Then, from the target machine, I downloaded the compiled exploit, gave it execution permissions and executed it.

<figure><img src="https://3648139271-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FDU2KcTfFp1xEzUDMyoAe%2Fuploads%2Fzwo995zUA1rwHTFjESn7%2Fimage.png?alt=media&amp;token=83a526a7-86b3-4438-ac42-ac20d720e4bb" alt=""><figcaption></figcaption></figure>

And this way I escalated privileges to root easily and read the root flag.

## New things learned <a href="#user-content-new-things-learned" id="user-content-new-things-learned"></a>

* The **environmental variables** should be checked every time.
* It’s important to check the OS and kernel version and look for vulnerabilities.